Seamless Auth

Open source passkey login you can run yourself.

Seamless Auth is the server, the SDKs, the admin dashboard and the CLI. Free under Apache-2.0, with no enterprise edition, and the first lane of a platform we're building in the open.

What is in it

  • Auth server: passkeys, magic links, one-time codes and OAuth
  • SDKs for Node, Go, Rust, Python, React, React Native and Angular
  • Admin dashboard for users, sessions and security events
  • CLI that scaffolds an app with auth already wired in
Product

Seamless Auth

Open-source, passwordless-only identity for teams that want a dedicated auth service and database instead of a shared identity pool.
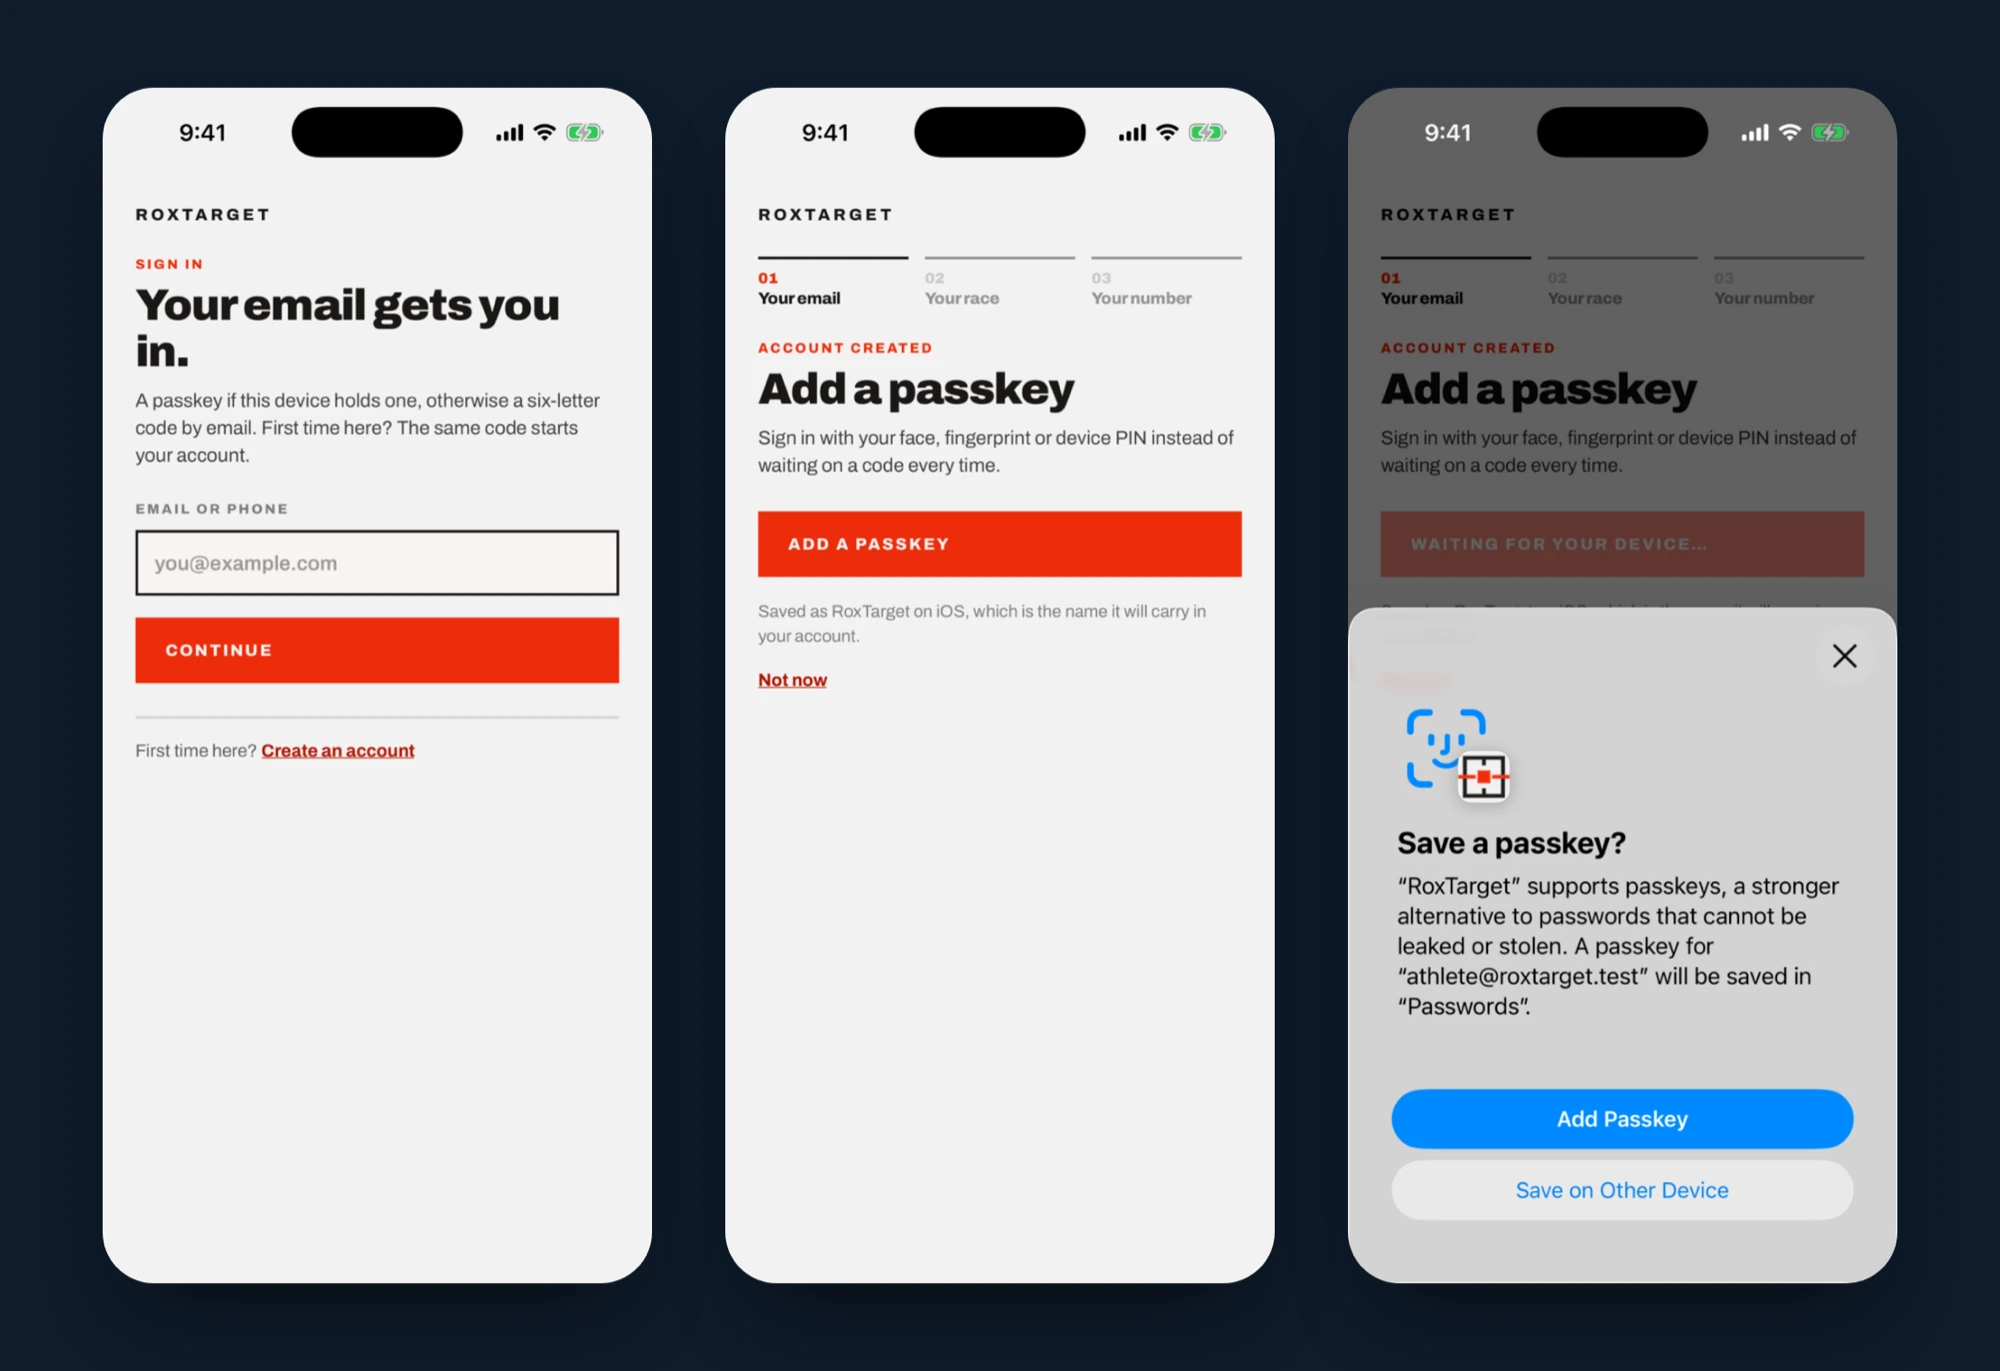
Three iPhone screens from RoxTarget: the sign-in screen, the add-a-passkey step, and the iOS Save a passkey sheet with Face ID.
Seamless Auth in production: signing in to RoxTarget with a passkey
The problem

Why this exists

Traditional authentication stacks are full of compromise. Shared identity pools blur security boundaries, password-based login introduces avoidable attack surface, and teams still lose time stitching the whole thing together.

The solution

What it does

Seamless Auth provides dedicated, passwordless identity with modern cryptography, deployment ownership, and a cleaner developer experience. It is built to remove password baggage instead of wrapping new UI around it.

How it helps

What you get from it.

  1. 01Each deployment gets its own dedicated authentication service with clear operational boundaries.
  2. 02Supports passkeys, WebAuthn, and asymmetric cryptographic login flows instead of passwords.
  3. 03Embeddable UI components avoid the usual redirect-heavy auth experience.
  4. 04Secure HTTP-only cookies handle sessions without pushing secrets into client storage.
  5. 05Recovery codes, self-service recovery and break-glass admins, so losing a passkey never locks anyone out.
  6. 06An OpenID Provider with hosted login and consent pages, so any app that speaks OpenID Connect can sign in without a Seamless SDK.
  7. 07Roles and permissions in the access token, checked by a guard in every adapter, plus signed webhooks and login hooks.
  8. 08Ships with SDKs for Node, Go, Rust, Python, React, React Native, Angular, Vue and Svelte, an admin dashboard, and a CLI.
Technical notes

Under the hood.

  • Each instance runs as its own service with its own Postgres database. Signing keys can load from AWS Secrets Manager.
  • Access tokens are RS256-signed JWTs. Refresh tokens are 32 random bytes, stored only as a keyed hash, and rotate on every use with reuse detection.
  • Browsers hold the session in httpOnly cookies set by your backend SDK. Mobile apps use bearer tokens.
  • Built-in JWKS endpoint so your APIs can verify tokens without calling the auth server.
  • Append-only audit log, hash-chained, with an integrity check and export.
  • Ships as a Docker image with docker-compose files for local and self-hosted runs.

Run your own identity in 5 mins.

One command scaffolds a web app, an API and a Seamless Auth server, already wired together. Free, open source, and yours to keep.

$ npx seamless-cli init my-app
Start the quickstartStar it on GitHub

Want help hosting or migrating? Say hello